You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
Critical PHP updates
- Thread starter ju5t
- Start date


Thank you! Succes, en sterkte, as we would say in DutchWe will be releasing patches for older PHP versions and a fix for PHP 8.1 compilation soon. We have them working but still running some tests.

Error: Failed to download metadata for repo 'epel': Cannot download repomd.xml: Cannot download repodata/repomd.xml: All mirrors were tried
executing 'dnf --quiet --assumeyes install gcc-c++ make autoconf pkgconfig openssl-devel systemd-devel krb5-devel libcurl-devel libpng-devel freetype-devel libwebp-devel libjpeg-devel libxslt-devel libsodium-devel libicu-devel sqlite-devel oniguruma-devel libffi-devel libtool-ltdl-devel libzip-devel' failed (attempt 1/3)
Error: Failed to download metadata for repo 'epel': Cannot download repomd.xml: Cannot download repodata/repomd.xml: All mirrors were tried
executing 'dnf --quiet --assumeyes install gcc-c++ make autoconf pkgconfig openssl-devel systemd-devel krb5-devel libcurl-devel libpng-devel freetype-devel libwebp-devel libjpeg-devel libxslt-devel libsodium-devel libicu-devel sqlite-devel oniguruma-devel libffi-devel libtool-ltdl-devel libzip-devel' failed (attempt 2/3)
It's legacy license

Scan your logs
Code:
zgrep -hiE 'php2shell|109618|109619' \
/var/log/nginx/domains/*.log* \
/var/log/httpd/domains/*.log* 2>/dev/null
Code:
zgrep -hiE 'auto_prepend_file|php://input|allow_url_include' \
/var/log/nginx/domains/*.log* \
/var/log/httpd/domains/*.log* 2>/dev/nullWere you able to download it? There’s nothing new in my yum.So far, CloudLinux have finished basically 1x version for many distros - PHP v7.4.
Thanks, what should I do now.Scan your logs
Code:zgrep -hiE 'php2shell|109618|109619' \ /var/log/nginx/domains/*.log* \ /var/log/httpd/domains/*.log* 2>/dev/null
Code:zgrep -hiE 'auto_prepend_file|php://input|allow_url_include' \ /var/log/nginx/domains/*.log* \ /var/log/httpd/domains/*.log* 2>/dev/null
149.102.239.83 - - [21/Oct/2026:14:27:52 +0200] "GET / HTTP/1.1" 301 4861 "-" "php2shell-checker/3.0 (authorized-scan)"
149.102.239.83 - - [21/Oct/2026:14:27:52 +0200] "GET / HTTP/1.1" 200 46619 "-" "php2shell-checker/3.0 (authorized-scan)"
149.102.239.83 - - [21/Oct/2026:14:27:53 +0200] "POST / HTTP/1.1" 200 46852 "-" "php2shell-checker/3.0 (authorized-scan)"
213.152.161.54 - - [21/Oct/2026:13:34:50 +0200] "HEAD / HTTP/1.1" 200 4832 "-" "Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 php2shell-probe"
213.152.161.54 - - [21/Oct/2026:13:45:35 +0200] "POST / HTTP/1.1" 200 99124 "-" "Mozilla/5.0 php2shell-sidfix"
You're absolutely right, and I completely agree. However, these servers won't be in use much longer, so upgrading the OS isn't really worth the time and effort.I don't want to be rude, but seriously, CentOS 7 is so outdated that you could do already an in-place upgrade to Almalinux.
I'm just looking for a temporary way to keep PHP patched and secure in the meantime.
We have heard that it has not been fully patched. Does anyone have more information on whether this is real and correct?, see below.
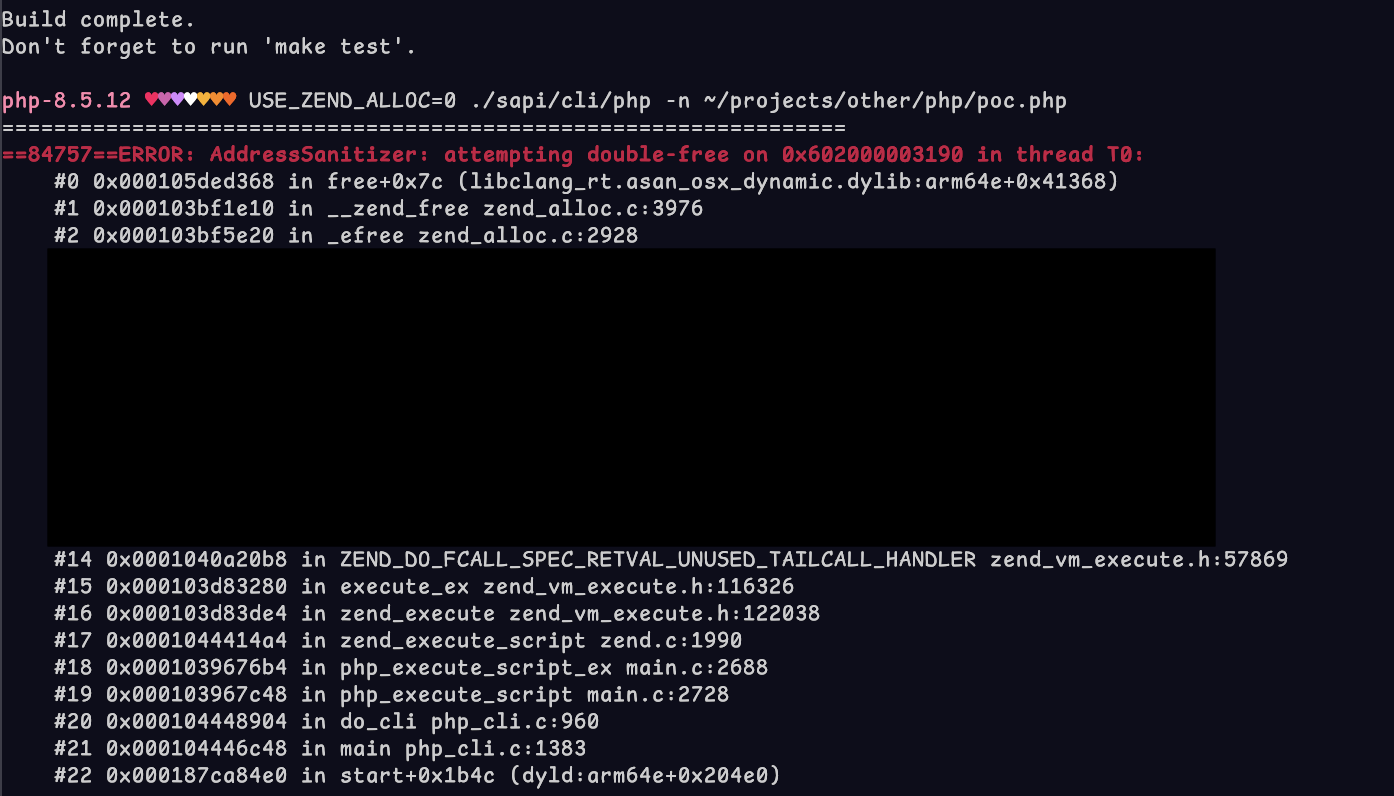


Looks like a separate memory bug, not yet fixed, that a specific PHP function triggers when a script calls it in a certain way. It isn't shown to be reachable through a simple web request.We have heard that it has not been fully patched. Does anyone have more information on whether this is real and correct?, see below.
Are you planning any updates or patches for CentOS 7.9? Many of us are still running it with DirectAdmin, and it would be helpful to know if any compatibility fixes or security updates are planned.A new build is released. It includes patches for older PHP versions (7.3, 7.2, 7.1, 7.0, 5.6) and also a small fix for the PHP 8.1 compilation.
A new build is released. It includes patches for older PHP versions (7.3, 7.2, 7.1, 7.0, 5.6) and also a small fix for the PHP 8.1 compilation.
GREAT WORK! Really appreciated! :-D
DirectAdmin > Plesk!