You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
new acme ssl system insufficient for handling domain name changes
- Thread starter digignosis
- Start date

Thank you, I don't have that config specified so it is still the default. I do understand that this case is a bit strange 
However: if my nameservers were used and someone removed the 'pop/smtp' DNS entry. With "preferer wildcard" turned off. What would happen then? I tried doing this with a test domain, and this is what I see after removing the DNS entries and removing the existing certificate:
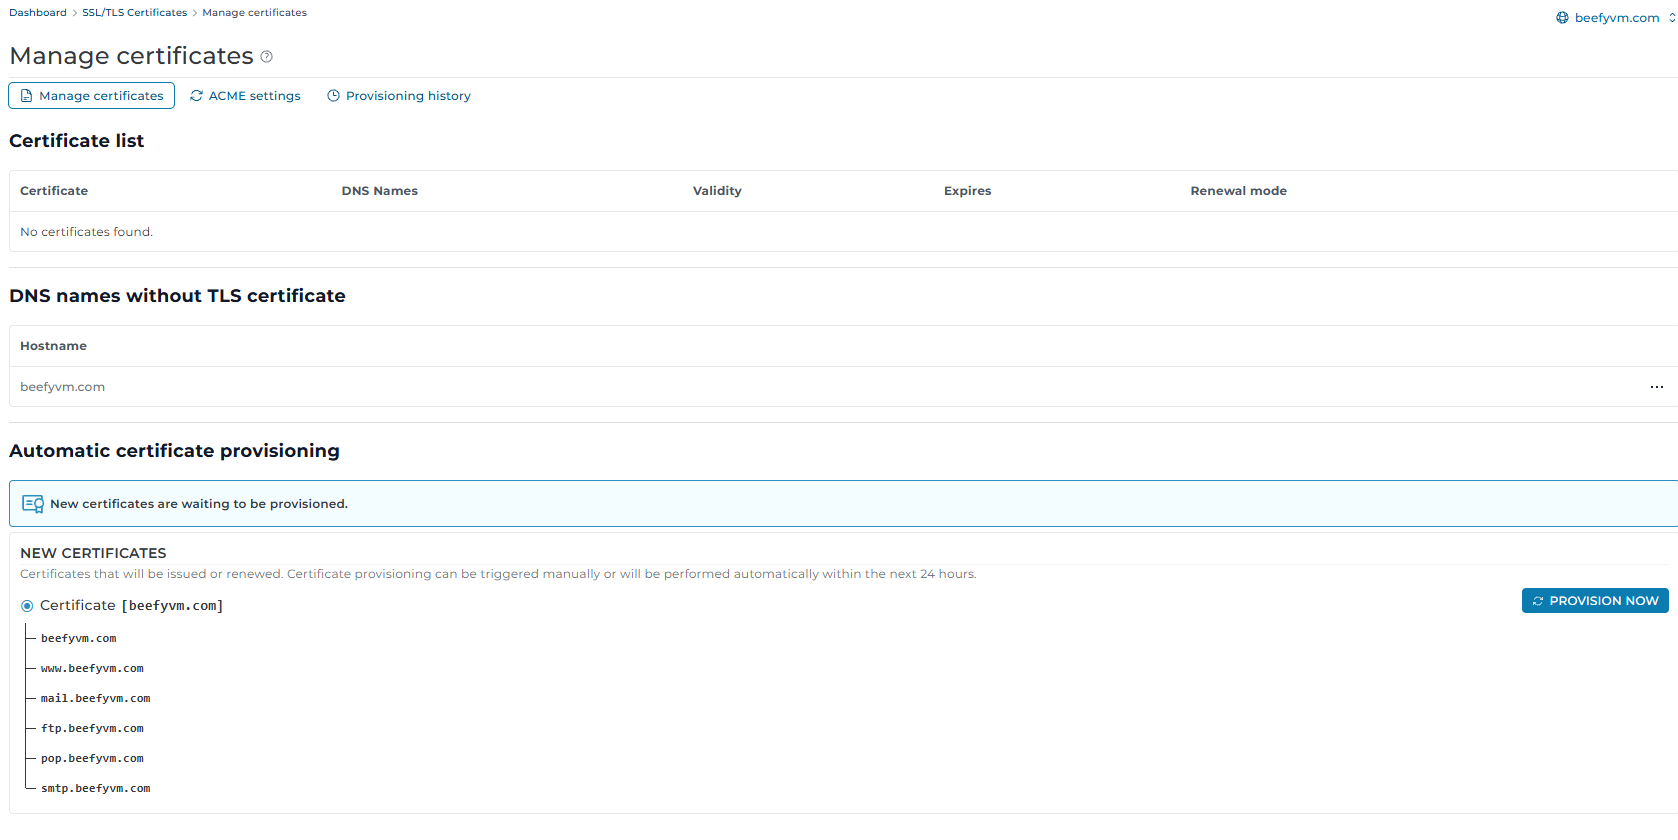
And when clicking "provision now" I indeed see that is it trying "pop/smtp". But (as expected) that fails.
So: let's say an end user has this case he can only get a cerficicate if he:
- goes for DNS validation
- re-adds pop/smtp
- asks me the server admin to remove pop/smtp from the letsencypt_list
That seems a bit strange right? Or is it possible to set the letsencypt_list to nothing? Does that allow the user to pick?
However: if my nameservers were used and someone removed the 'pop/smtp' DNS entry. With "preferer wildcard" turned off. What would happen then? I tried doing this with a test domain, and this is what I see after removing the DNS entries and removing the existing certificate:
And when clicking "provision now" I indeed see that is it trying "pop/smtp". But (as expected) that fails.
2026-09-17T11:44:13.562399396+02:00 ERROR Error error="renew certificate: could not obtain the certificate for \"beefyvm.com\": resolver: one or more domains had a problem: [pop.beefyvm.com: invalid authorization: acme: error: 400 :: urn:ietfarams:acme:error:dns :: DNS problem: NXDOMAIN looking up A for pop.beefyvm.com - check that a DNS record exists for this domain; DNS problem: NXDOMAIN looking up AAAA for pop.beefyvm.com - check that a DNS record exists for this domain] [smtp.beefyvm.com: invalid authorization: acme: error: 400 :: urn:ietf
So: let's say an end user has this case he can only get a cerficicate if he:
- goes for DNS validation
- re-adds pop/smtp
- asks me the server admin to remove pop/smtp from the letsencypt_list
That seems a bit strange right? Or is it possible to set the letsencypt_list to nothing? Does that allow the user to pick?

- Joined
- Aug 30, 2021
- Messages
- 1,488
The new ACME system performs the HTTP challenge test for each subdomain before it runs the lego tool.
I think the local dns resolver still have the records pop subdomain in the cache. So local http test was successful, however the LE servers rejected it. If you retry the same test after a while or clear DNS resolver cache th DA will stop trying issuing certificate for the non functional subdomain.
I think the local dns resolver still have the records pop subdomain in the cache. So local http test was successful, however the LE servers rejected it. If you retry the same test after a while or clear DNS resolver cache th DA will stop trying issuing certificate for the non functional subdomain.
TTL is set to 3600 it has been 2 hours and 15 minutes.
A `dig` from the DA machine informs me that the `pop` record does not exist. However I still see the same when requesting a certificate. Turning ACME off and on again also does not help.
Does it have a separate cache or something?
---
And may I suggest re-adding some feature to pick yourself. This is very hard to explain to a customer if he wants to to some maintenance (e.g. remove unused DNS entries) and must wait till some cache is expired before requesting a SSL certificate.
A `dig` from the DA machine informs me that the `pop` record does not exist. However I still see the same when requesting a certificate. Turning ACME off and on again also does not help.
Does it have a separate cache or something?
---
And may I suggest re-adding some feature to pick yourself. This is very hard to explain to a customer if he wants to to some maintenance (e.g. remove unused DNS entries) and must wait till some cache is expired before requesting a SSL certificate.
Last edited:
- Joined
- Aug 30, 2021
- Messages
- 1,488
There is no additional caching inside DA.
What DA does under the hood is something similar to create
This means there are multiple ways you could trick this test into being successful even if the subdomain from outside the server is non-functional. For example:
On servers without configuration problems local HTTP challenge test works just as well as external HTTP challenge test (from ACME server). In practice users never encounter the DNS caching problems. If domain never had functional subdomain record, the test fails and ACME system will not try to issue cert for it. If they were once functional, it means they already have a valid cert for it. Next time certificate needs to be renewed the non-functional subdomains are omitted.
The situation when domain was functional 5 minutes ago but now is not functional happens only when testing things out or if server have some problems and the local HTTP challenge test can not be performed reliably.
What DA does under the hood is something similar to create
/var/www/html/.well-known/{rand-name} file and the make a request to curl http://sub.example.com/.well-known/acme-challenge/{rand-name}. In other words it does the same HTTP challenge test that ACME would perform but everything is executed locally (inside the server).This means there are multiple ways you could trick this test into being successful even if the subdomain from outside the server is non-functional. For example:
- Adding records for subdomains to
/etc/hosts. - Using locally running bind as local recursive resolver (having
nameserver 127.0.0.1in the/etc/resolv.conf) and using external nameservers for this domain. - Using 3rd-party caching recursive resolver that returns stale data.
On servers without configuration problems local HTTP challenge test works just as well as external HTTP challenge test (from ACME server). In practice users never encounter the DNS caching problems. If domain never had functional subdomain record, the test fails and ACME system will not try to issue cert for it. If they were once functional, it means they already have a valid cert for it. Next time certificate needs to be renewed the non-functional subdomains are omitted.
The situation when domain was functional 5 minutes ago but now is not functional happens only when testing things out or if server have some problems and the local HTTP challenge test can not be performed reliably.